By Kaaren Morrissey and Max Aldred
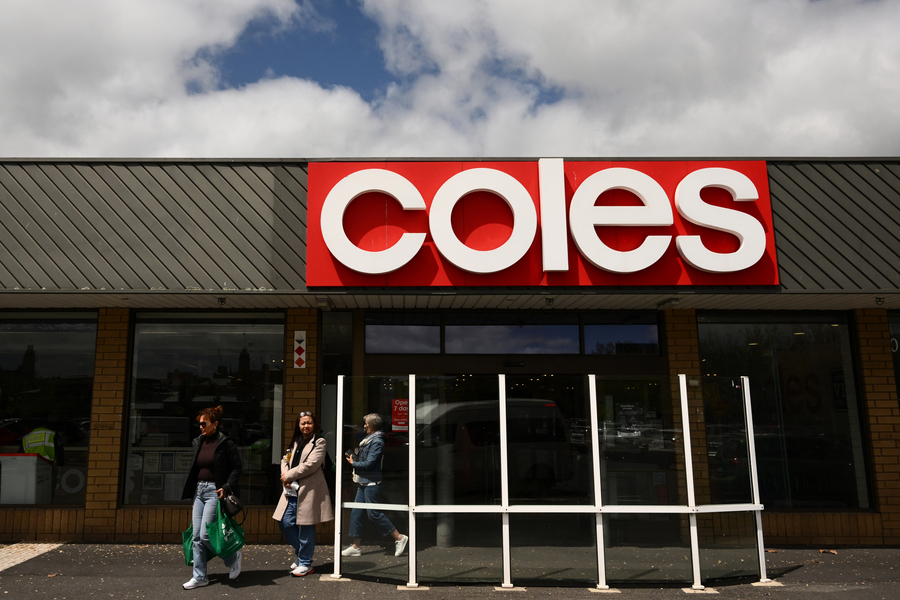
Australia’s second-largest supermarket chain has urged customers to take basic online precautions after it was targeted in a cyber attack.
Coles revealed it was investigating a cyber security incident on Monday morning but said there was no evidence that any data was compromised.
Coles is also investigating reported issues with Liquorland’s click-and-collect service.
“We have not identified any evidence that customer, team or supplier data has been compromised or removed from Coles’ systems,” Coles said in a statement.
The supermarket giant asked customers to continue to be wary of scams as investigations continue.
“We advise everyone to take basic online precautions and recommend remaining vigilant to suspicious links, attempts to solicit personal information … and potential scam activity,” a customer notice said.
“Coles will never ask you to provide your password or other sensitive account information through an unsolicited email or SMS.”
The retailer said shoppers were able to shop as normal both in store and online.
The grocer apologised to its customers for any concerns they might have at “a time of increasing cyber incidents in Australia and around the world”.
“We have security measures in place to protect customer and supplier accounts and are continuing to closely monitor our system,” it said.
“We recommend you regularly update your password with a strong, unique password for your account and not reuse the same password across multiple services.”
The supermarket is investigating the attack with assistance from the Australian Cyber Security Centre and global security experts.
Both the public and private sectors have been targeted in recent data breaches and cyber attacks.
In October, a suspected overseas hacker entered and exfiltrated data related to third-party dental providers from a NSW Health server.
Qantas in November had to notify customers of a cyber attack on an international third-party travel technology provider, Amadeus.
An artificial intelligence agent also broke into the NSW Parks and Wildlife website and Medicare statistics in 2026, which was discovered in October.
Experts previously told AAP that AI was turbocharging bad actors’ abilities, and ushering in a new age of cyber threats.
Single commands to AI agents are reaping extensive and rapid damage, researchers for international security firm Elastic observed.
Agents could execute thousands of actions with limited intervention and work through flawed and failed attempts, they said a report.
Security engineer Brent Sargent warned attacks on government and government-aligned organisations faced the greatest risk.
News all day, every day at CityNewsQBN.com.au.

Leave a Reply